

Overview
Lumos supports two types of Custom Roles:- Custom Org Roles apply organization-wide. Use these to give users a tailored combination of permissions across all of Lumos. Examples include an Access Review Manager, Read-Only Auditor, Helpdesk Viewer, or Procurement Partner.
- App Resource Roles (Beta) apply to specific apps when assigned. Use these to customize what an App Admin can do on a particular app. For example, allow a team lead to approve access requests for an app but prevent them from changing the app’s provisioning workflows.
- Allow users to access only the parts of Lumos that matter to them, like Access Reviews, AppStore, Identities, Vendors, or Integrations
- Choose whether they can view or manage each module with coarse-grained permissions
- Create purpose-built roles such as Access Review Manager, Read-Only Auditor, Helpdesk Viewer, or Procurement Partner
- Customize App Admin capabilities on a specific app instead of granting the full App Admin bundle
- Assign these roles to users confidently while maintaining least-privilege and reducing operational risk
Step 1: View default roles
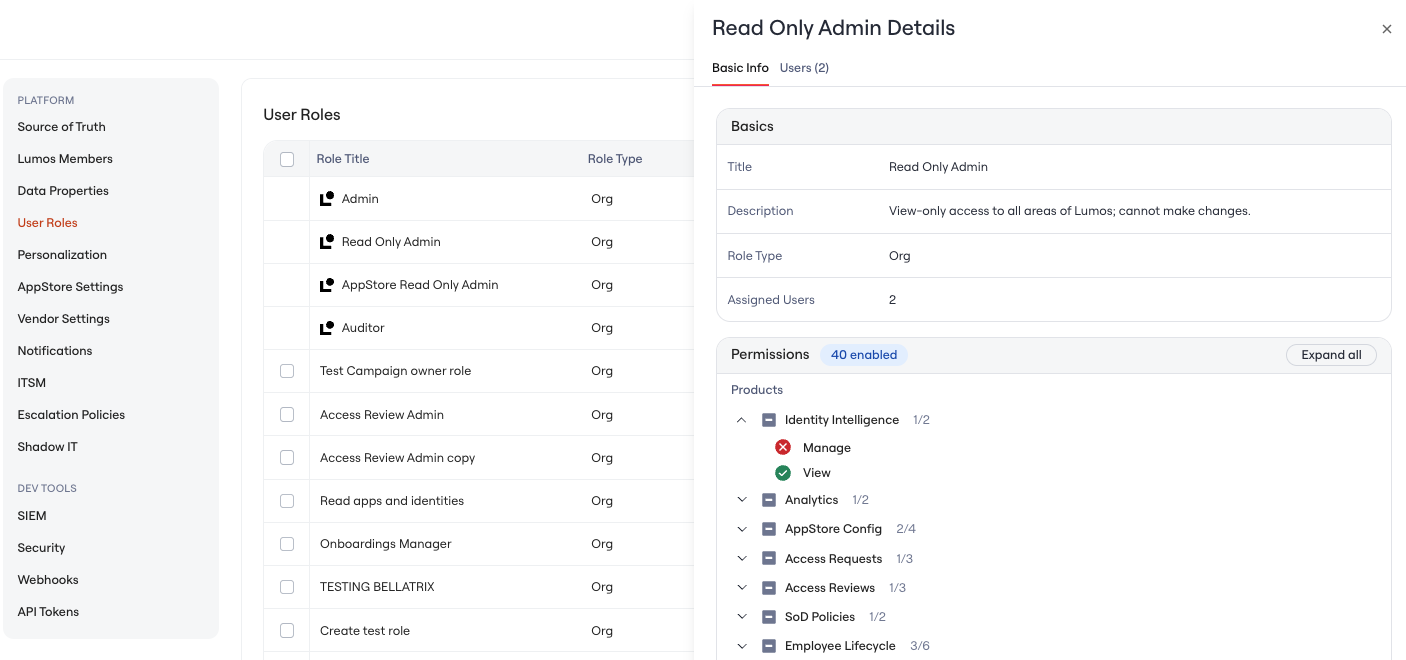
You can view the scope of all legacy Lumos default roles, along with the members assigned to them, in one centralized place under Settings → User Roles.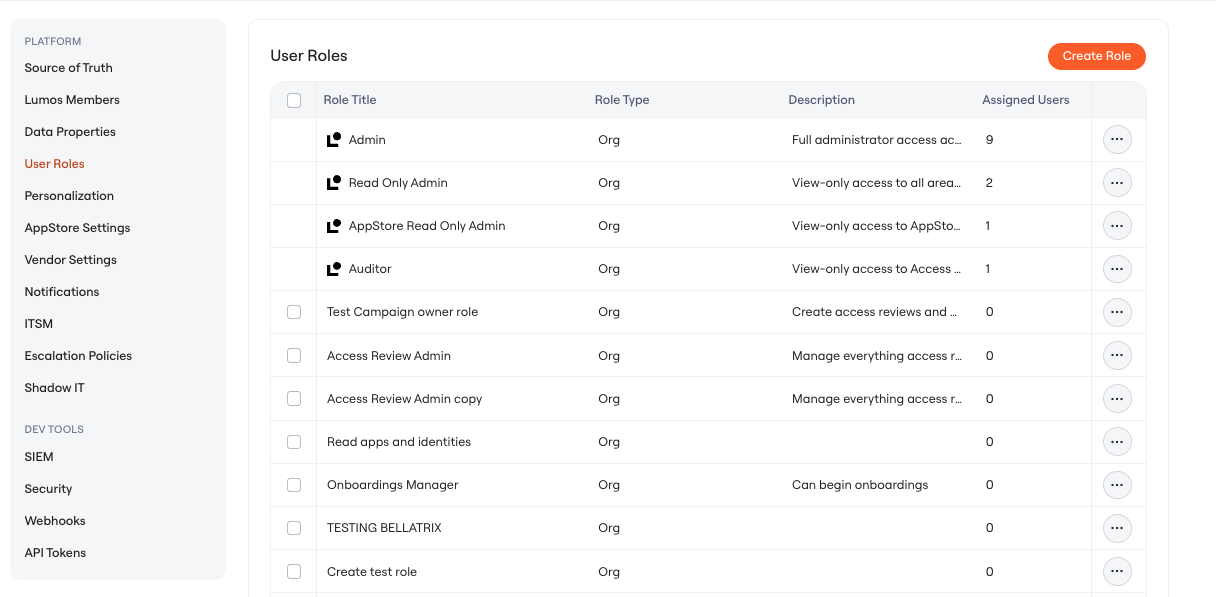
Step 2: Create a Custom Role
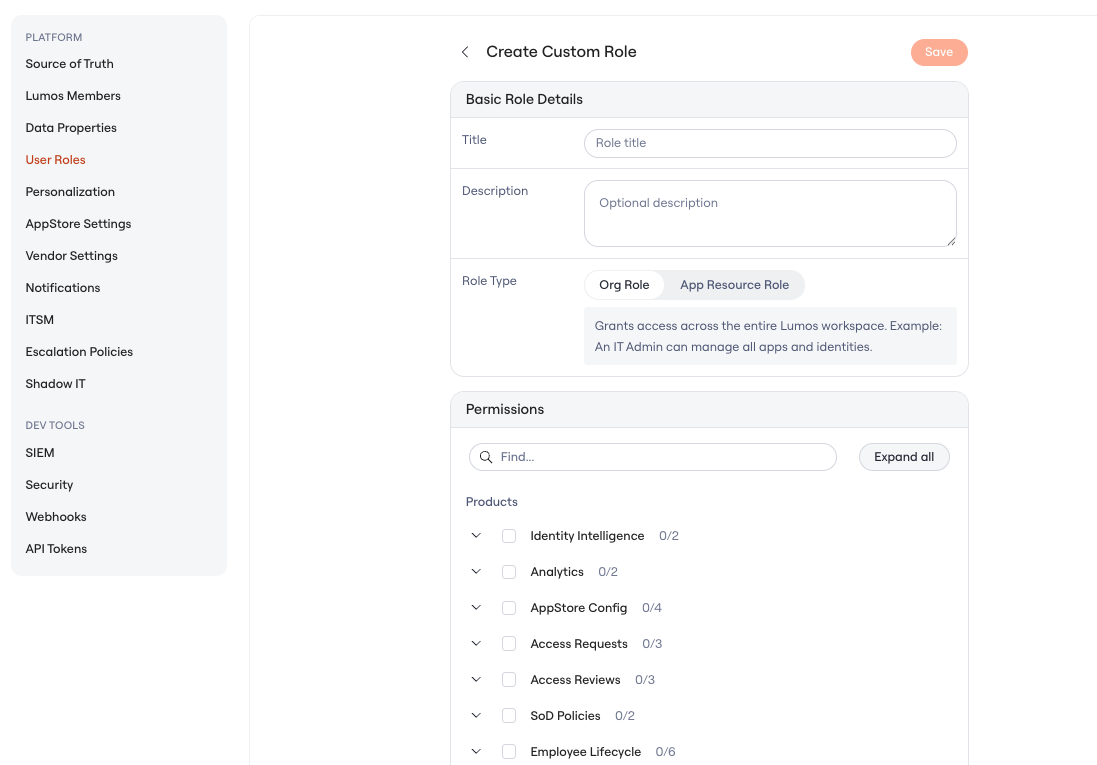
Select Create Role to open the configuration page. In Basic Role Details, enter:- Title — the name of the role as it will appear in the User Roles table and the Access Level picker
- Description — optional, but recommended so other admins know what the role is for
- Role Type — choose between Org Role and App Resource Role
Choosing the right Role Type
- Org Role — grants permissions across the entire organization. The user holds the role regardless of which application or resource they are working with.
- App Resource Role — grants permissions only on specific applications when assigned. The user holds the role for the apps you assign it to, and no others. “Grants access only to specific resources when assigned. Example: An App Admin can manage GitHub, but not other apps.”
Configure permissions
In the Permissions section, choose the appropriate product surfaces and coarse-grained permissions such as View, Manage, or Create.- For an Org Role, the catalog covers Products (Identity Intelligence, Analytics, AppStore Config, Access Requests, Access Reviews, SoD Policies, Employee Lifecycle), Inventory (Apps, Identities, Non-Human Identities, Vendor Agreements, Spend Records, Found Documents, Access Policies, Knowledge Hub), and Workspace (Activity Logs, MCP Governance, On-Prem Agents, Org Settings, Custom Attributes, Tasks).
- For an App Resource Role, the catalog is intentionally narrower and includes only the permissions that make sense at a per-app scope: AppStore Config, Access Requests, Apps, and Tasks. At the bottom of the permission picker the UI shows: “Additional permissions are not supported for this role.”
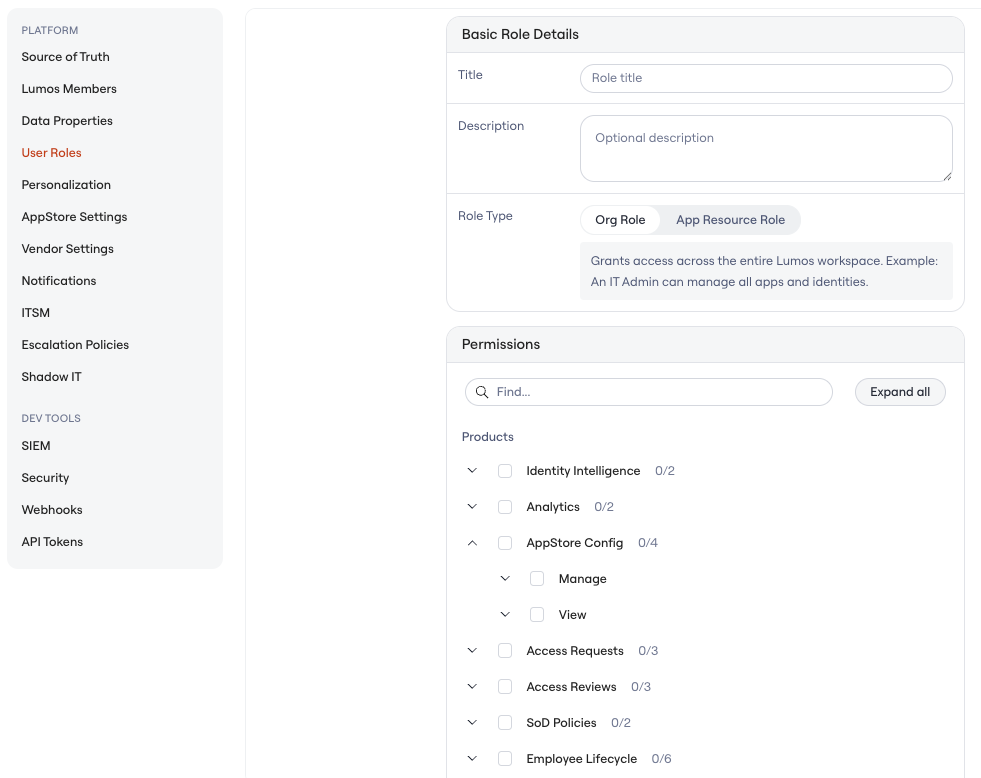
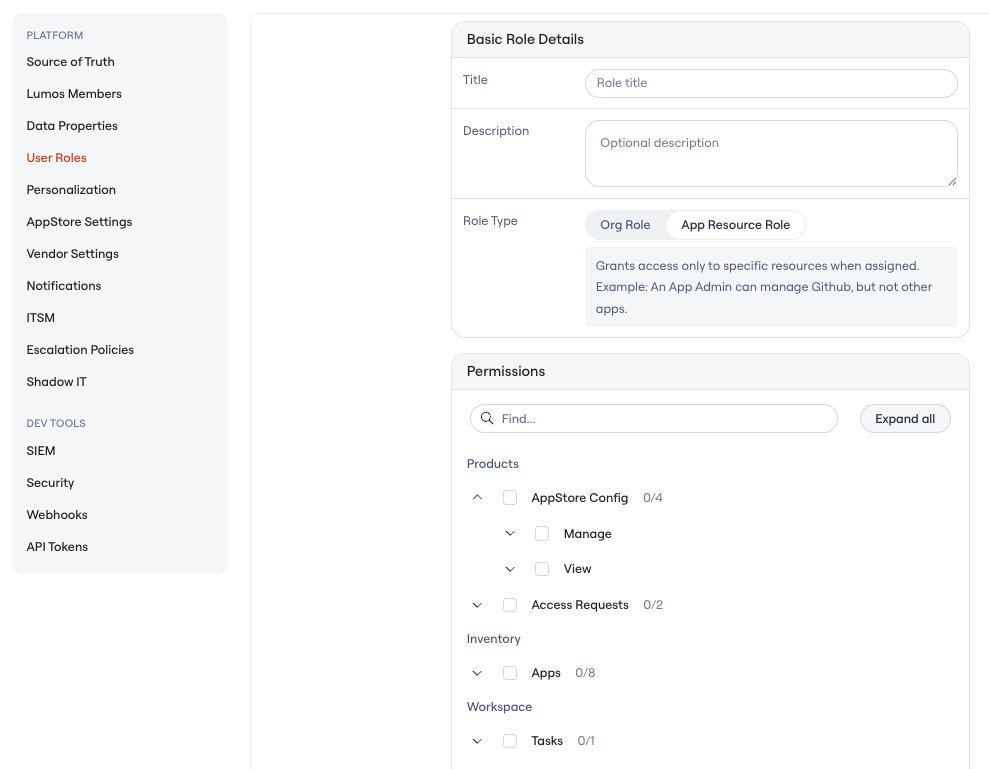 Once saved, the new custom role appears in the User Roles table.
Step 3: Assign the role
How you assign the role depends on the role type.Assign a Custom Org Role
Assign org roles from the Settings page → Lumos Members tab by using the dropdown in the Access Level column. A user can hold multiple roles at once, and the permissions are additive.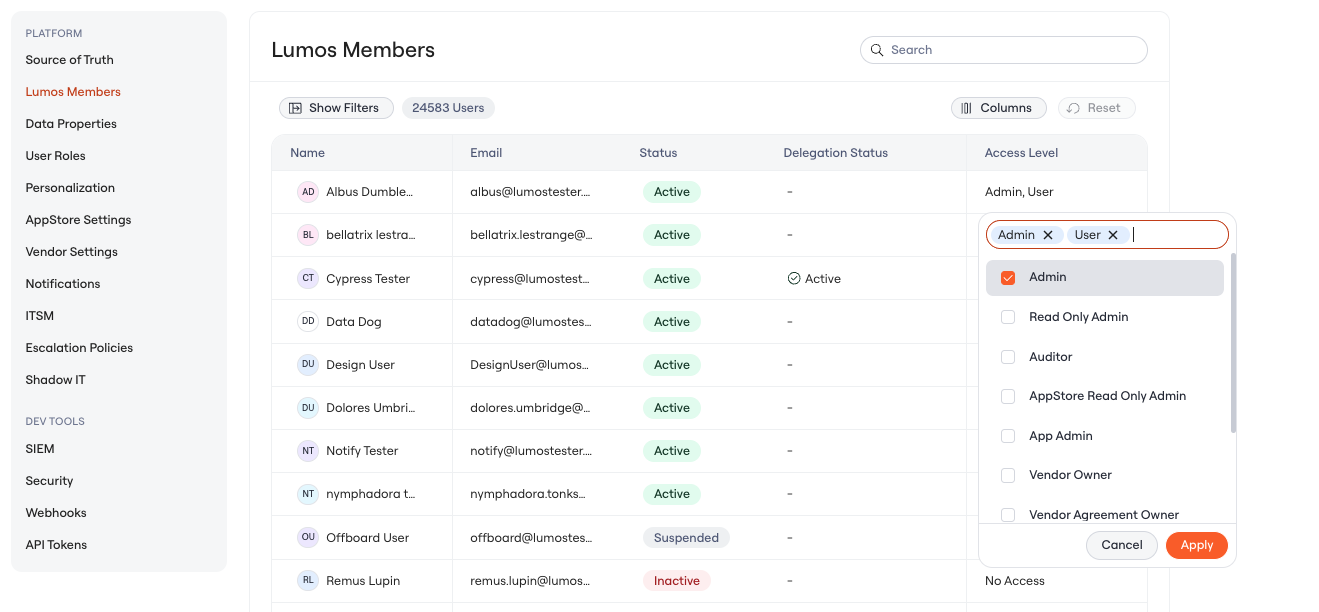
Assign an App Resource Role
App Resource Roles are assigned per app from the app’s page. Open the app in Lumos, find the role-assignment area, and assign the role to a user or group. The same App Resource Role can be assigned to different users on different apps independently.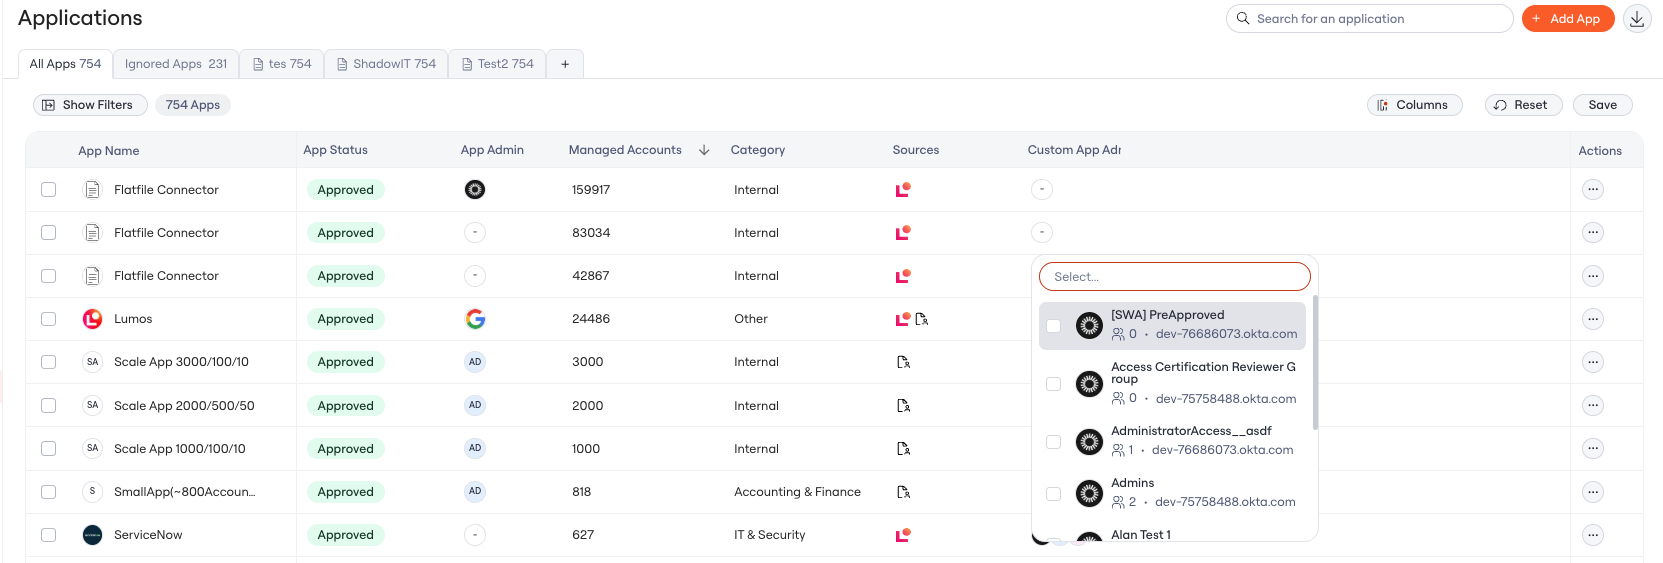
Behavior and limits
- Admin only. Only users with the Admin role can create, edit, or delete Custom Roles.
- Edits take effect on next session. When you change a Custom Role’s permissions, assigned users see the updated permissions the next time they log in or refresh their session.
- Deletion is allowed. If you delete a Custom Role, users who held that role fall back to the default User role.
- No limits today. There is no cap on the number of Custom Roles per tenant or the number of users that can be assigned a given role.
- Partial API support. Custom Role creation and editing are not yet available via the public Lumos API. You can grant and revoke Custom Org Roles through the existing role API endpoints, the same way as built-in roles. App Resource Role assignments are not yet supported via the API.
- No Activity Log audit today. Custom Role create, edit, delete, and assignment events are not yet captured in the Activity Log.
- Reserved names. Built-in Lumos role names are reserved and cannot be used as Custom Role titles.
Tips and examples
Example Org Roles
- Access Review Manager — Manage access reviews, create review campaigns, manage review assignments. Cannot configure integrations or change org settings.
- Read-Only Auditor — View access reviews, view activity logs, generate review reports. No write access anywhere.
- Helpdesk Viewer — View apps, view accounts, view access requests, view tasks. Cannot make changes.
- Procurement Partner — View and manage vendor agreements, manage spend records, view dashboards. No access to AppStore configuration or integrations.
Example App Resource Roles
- Approvals-only App Admin — Manage and view AppStore Config (Approvals), manage Access Requests, view Apps (Accounts, Basic Details, Workflows). The team lead can act on approvals for the assigned app but cannot edit provisioning workflows or change integration settings.
- Entitlement Editor — Manage and view Apps (Permissions, Basic Details). The app owner can clean up entitlement names and descriptions, but cannot change workflows, approvals, or integration settings.
- App Viewer — View Apps (Accounts, Basic Details, Workflows), View AppStore Config. The finance team can audit configuration on a specific app without making changes.