

Overview
The Entra NHI Security Analyst examines the non-human identity landscape in Microsoft Entra ID and surfaces the combinations of factors that create real, exploitable risk. It is one of the Identity Agent Force agents. For the big picture and how agents work, see the Identity Agent Force Overview.What it analyzes
The agent examines the full non-human identity landscape in Entra ID across five data domains.
The agent deliberately excludes identities that are not actionable findings: vendor-managed multi-tenant service principals (Microsoft, Salesforce, Okta, where multi-tenancy is by design), Microsoft first-party service principals, disabled service principals, and actively-used NHIs with properly managed credentials.
What you will find
Findings that fail verification are dismissed automatically: permissions that were requested but never granted, expired credentials, and disabled identities never reach your team.
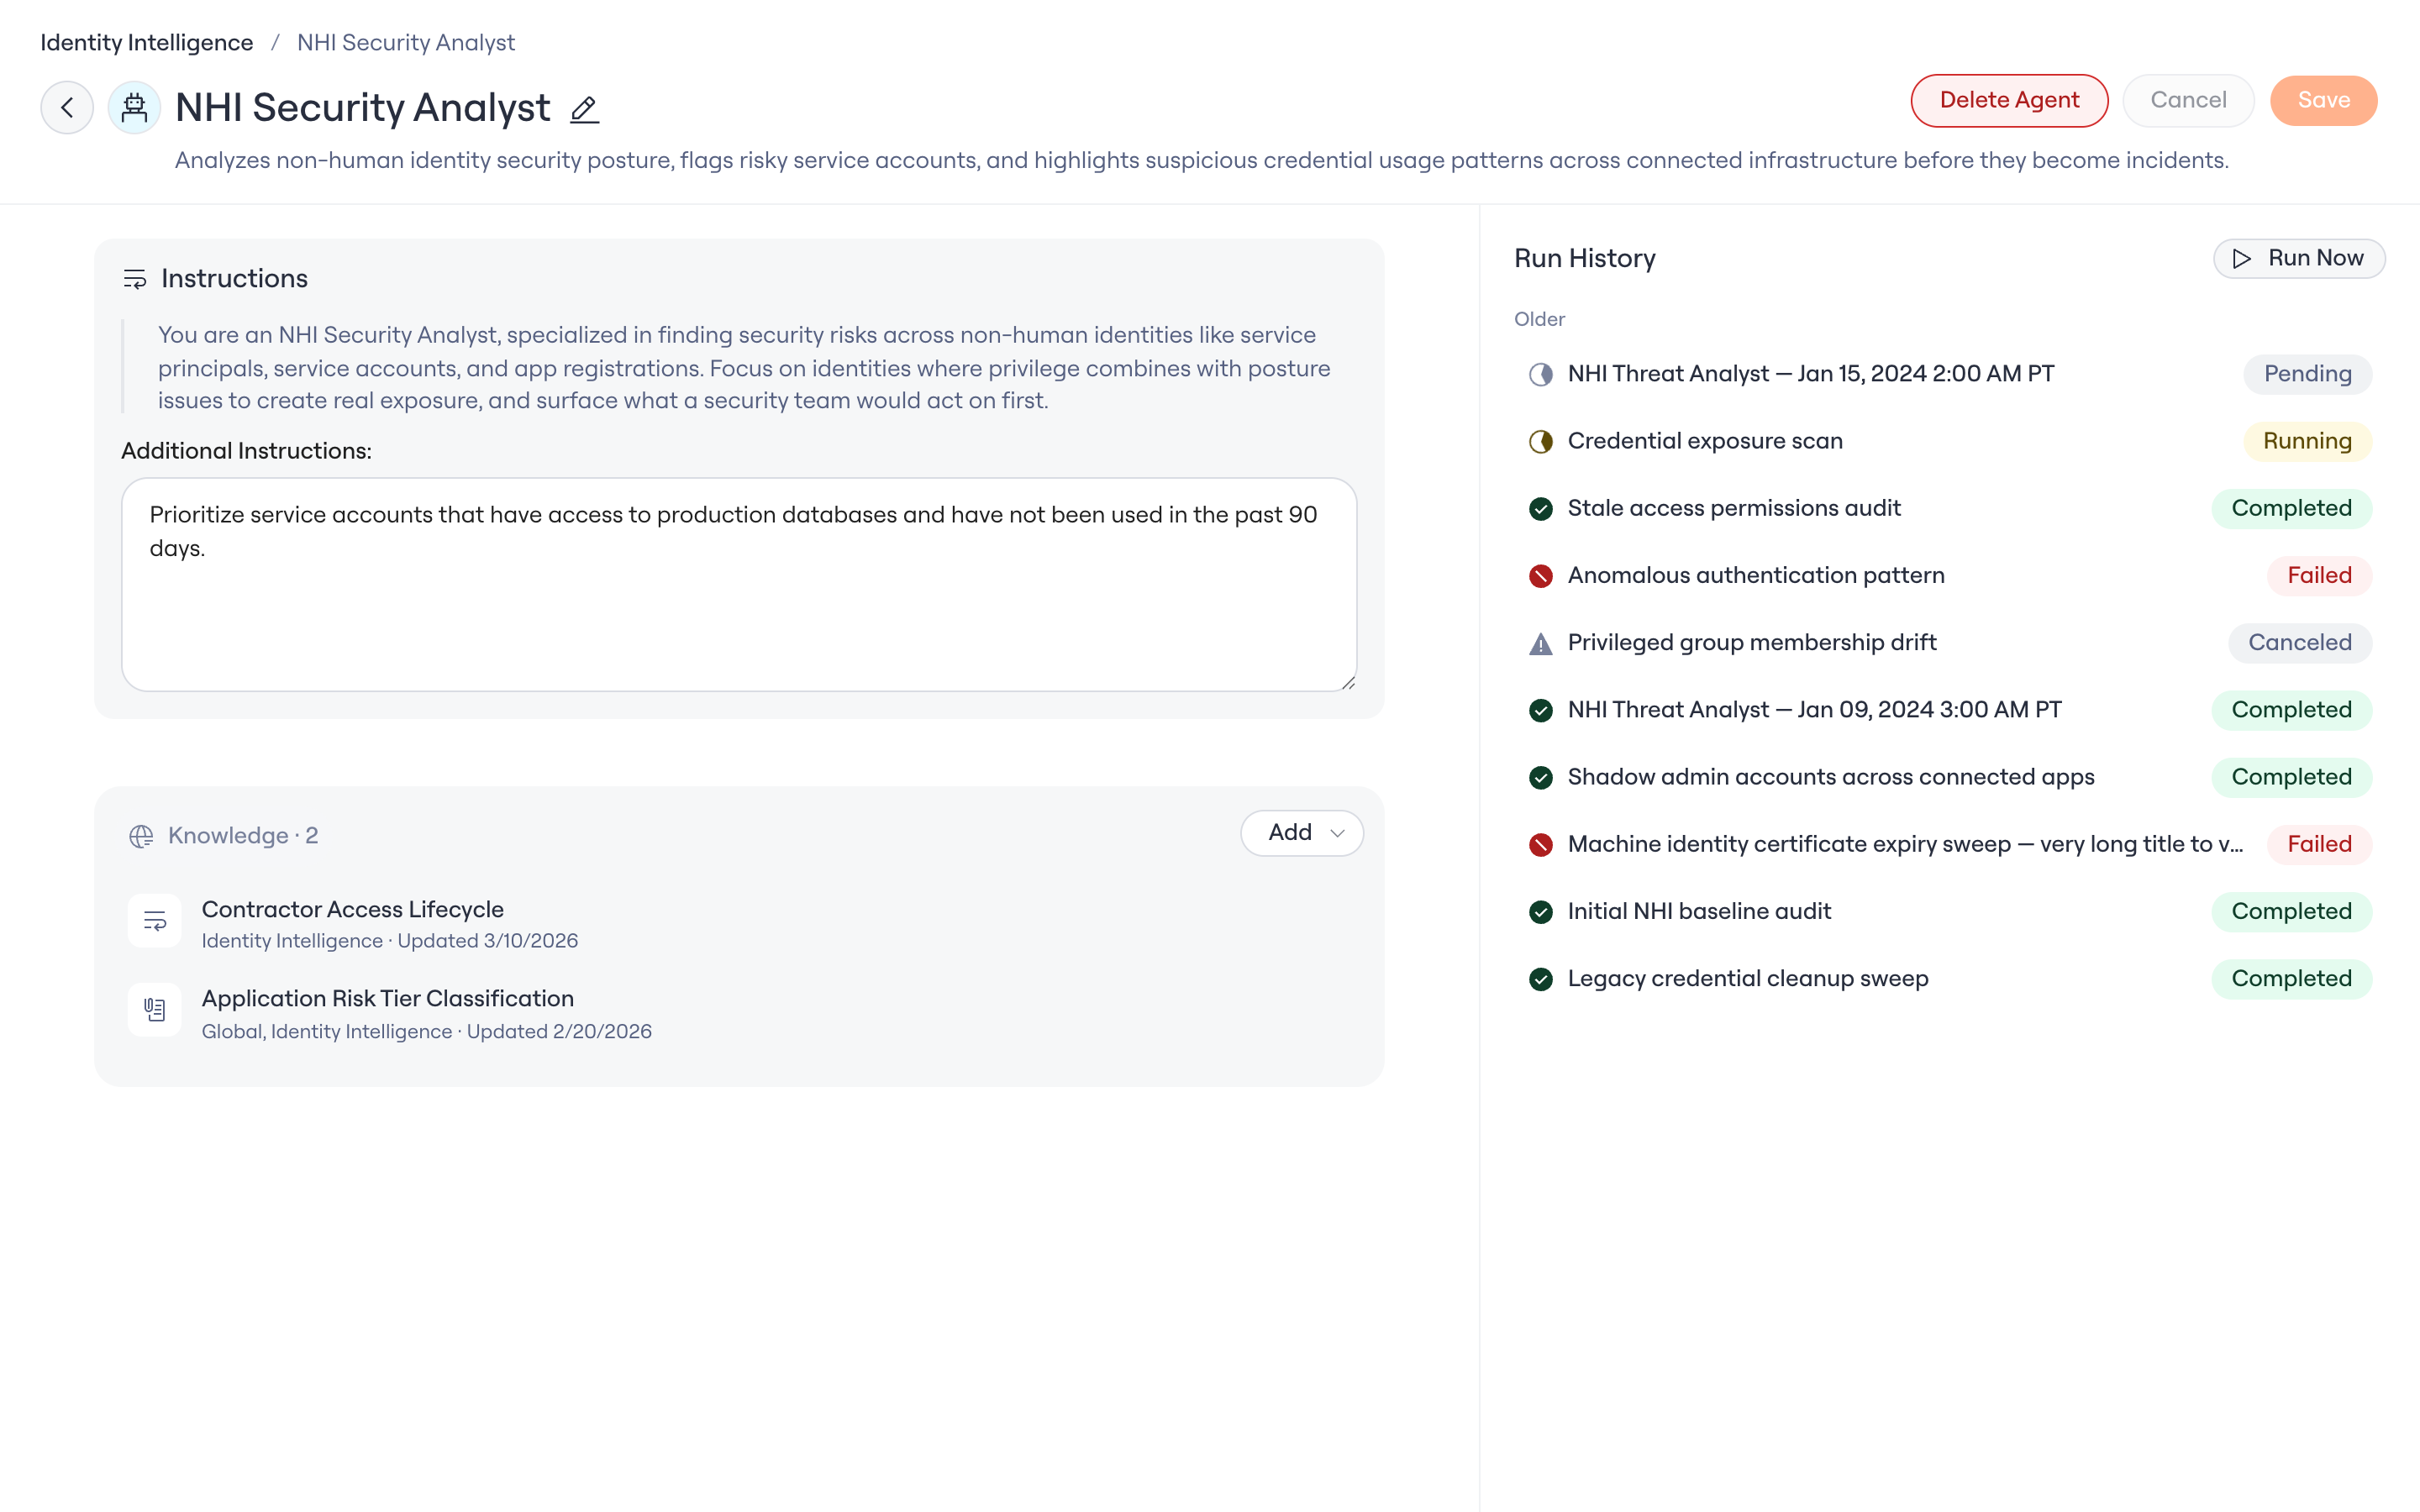
The Entra NHI Security Analyst configuration
Connect and get started
- Connect Microsoft Entra ID. See Connecting Microsoft Entra ID (NHI). The analysis is read-only: it queries the Microsoft Graph API with scoped application permissions.
- Create an agent with the Entra NHI Security Analyst specialization (see the overview for the create flow).
- Open the Identity Agent Force page to review findings, assign owners, and launch each Issue’s remediation workflow.
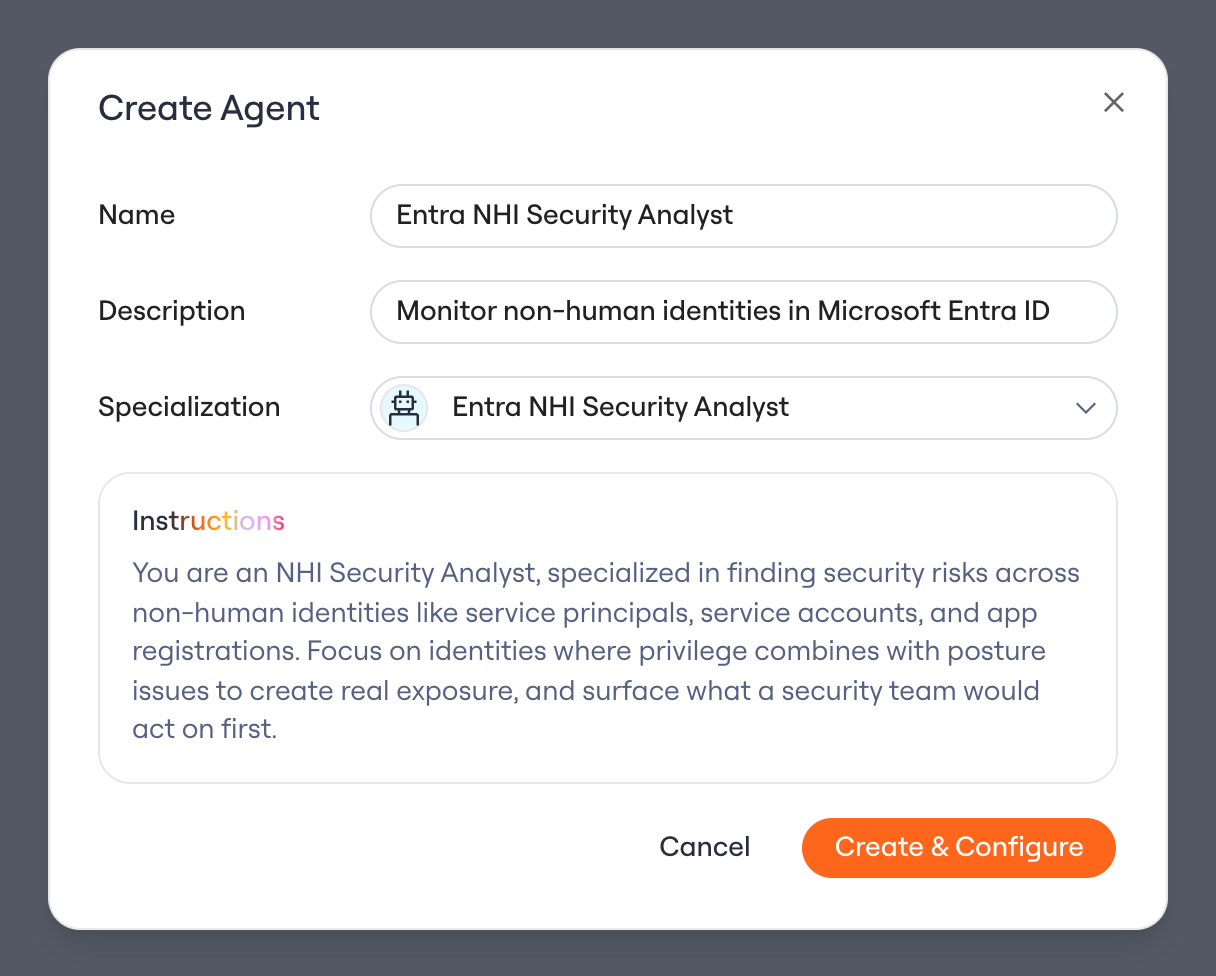
Creating the Entra NHI Security Analyst agent