

Overview
The AWS NHI Threat Hunter examines non-human identities across your AWS accounts and surfaces the combinations of factors that create real, exploitable risk. It is one of the Identity Agent Force agents. For the big picture and how agents work, see the Identity Agent Force Overview.What it analyzes
The agent examines non-human identities across your AWS accounts: IAM, federation, external resource exposure, and compromise signals.
The agent deliberately excludes anything that is not actionable or would cross into data-plane territory: AWS-managed service-linked roles with unmodified trust policies, AWS-managed KMS keys, and any action that would read content (secret values, S3 objects, Lambda results, CloudTrail event bodies, log contents, or environment variables).
What you will find
The AWS profile targets Critical and High severity only, to keep the permission ask small and avoid alert fatigue. Findings that fail verification (accounting for permissions boundaries, session duration limits, and inactive assignments) are dismissed automatically.
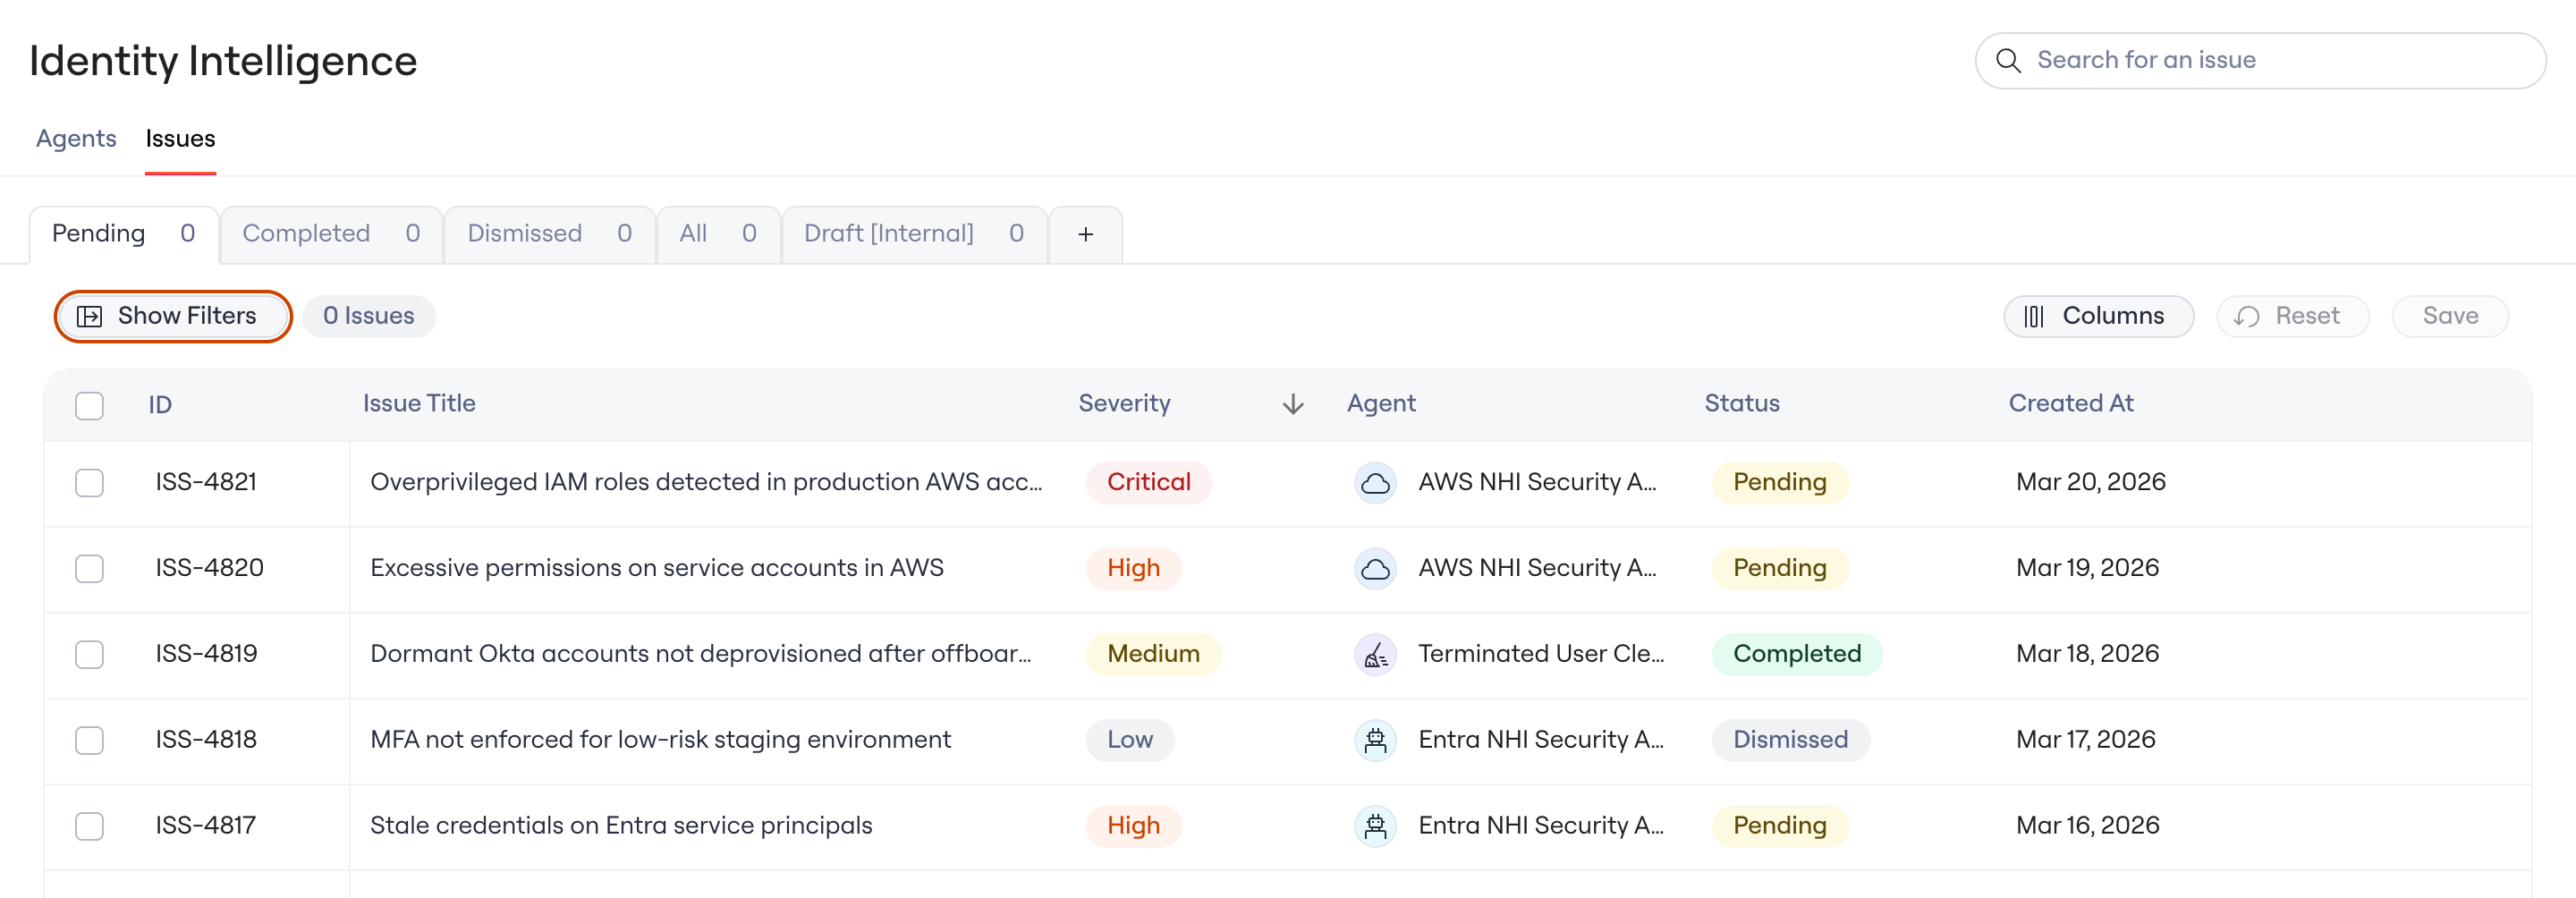
AWS NHI Threat Hunter issues on the Identity Agent Force page
Connect and get started
- Connect AWS using the AWS NHI (Graph) connector, which is a separate connector from the traditional AWS IAM and AWS Identity Center connectors. See Connecting to AWS IAM Identity Center (NHI).
- Create an agent with the AWS NHI Threat Hunter specialization (see the overview for the create flow).
- Open the Identity Agent Force page, review each Issue, and launch its remediation workflow.
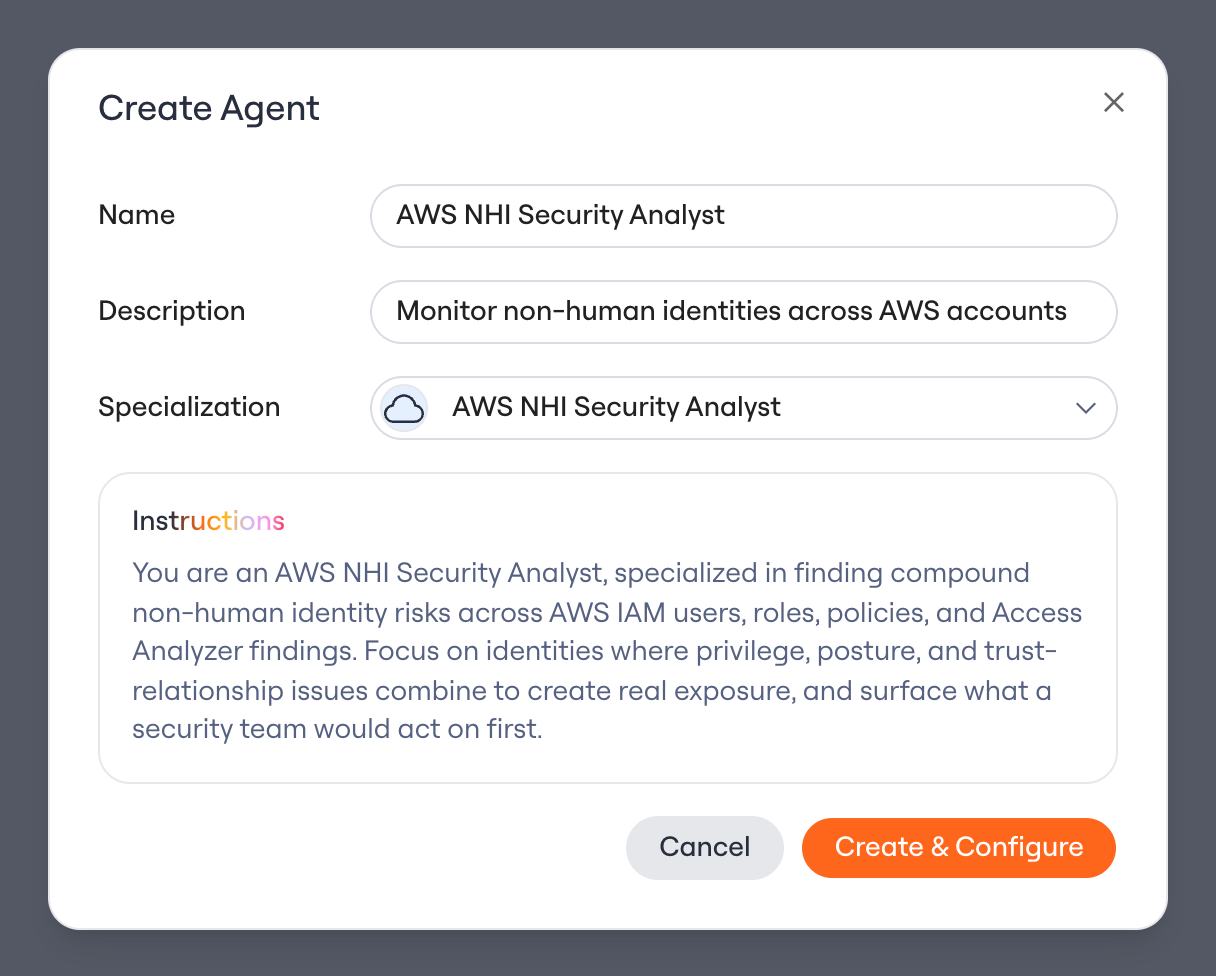
Creating the AWS NHI Threat Hunter agent