

1. Open the policy from the link you were sent
Lumos does not yet send a notification when a policy is shared with you, so whoever shared it will send you a link. If you need to log in, use your Single Sign-On (SSO) login or email. The policy is read-only for you. You can view it and leave comments. You cannot change the access, rename the policy, publish it, or share it with anyone else, so nothing breaks while you look around.2. Read what the policy grants
Three sections tell you everything you need:- Policy Conditions: who the policy covers. For example, everyone whose email is on your company domain, or everyone on a specific team.
- Business Justification: why the policy exists, written by the team that owns it.
- Grant Apps & Permissions: the apps, groups, and roles the covered employees get automatically. This is the part you are reviewing.
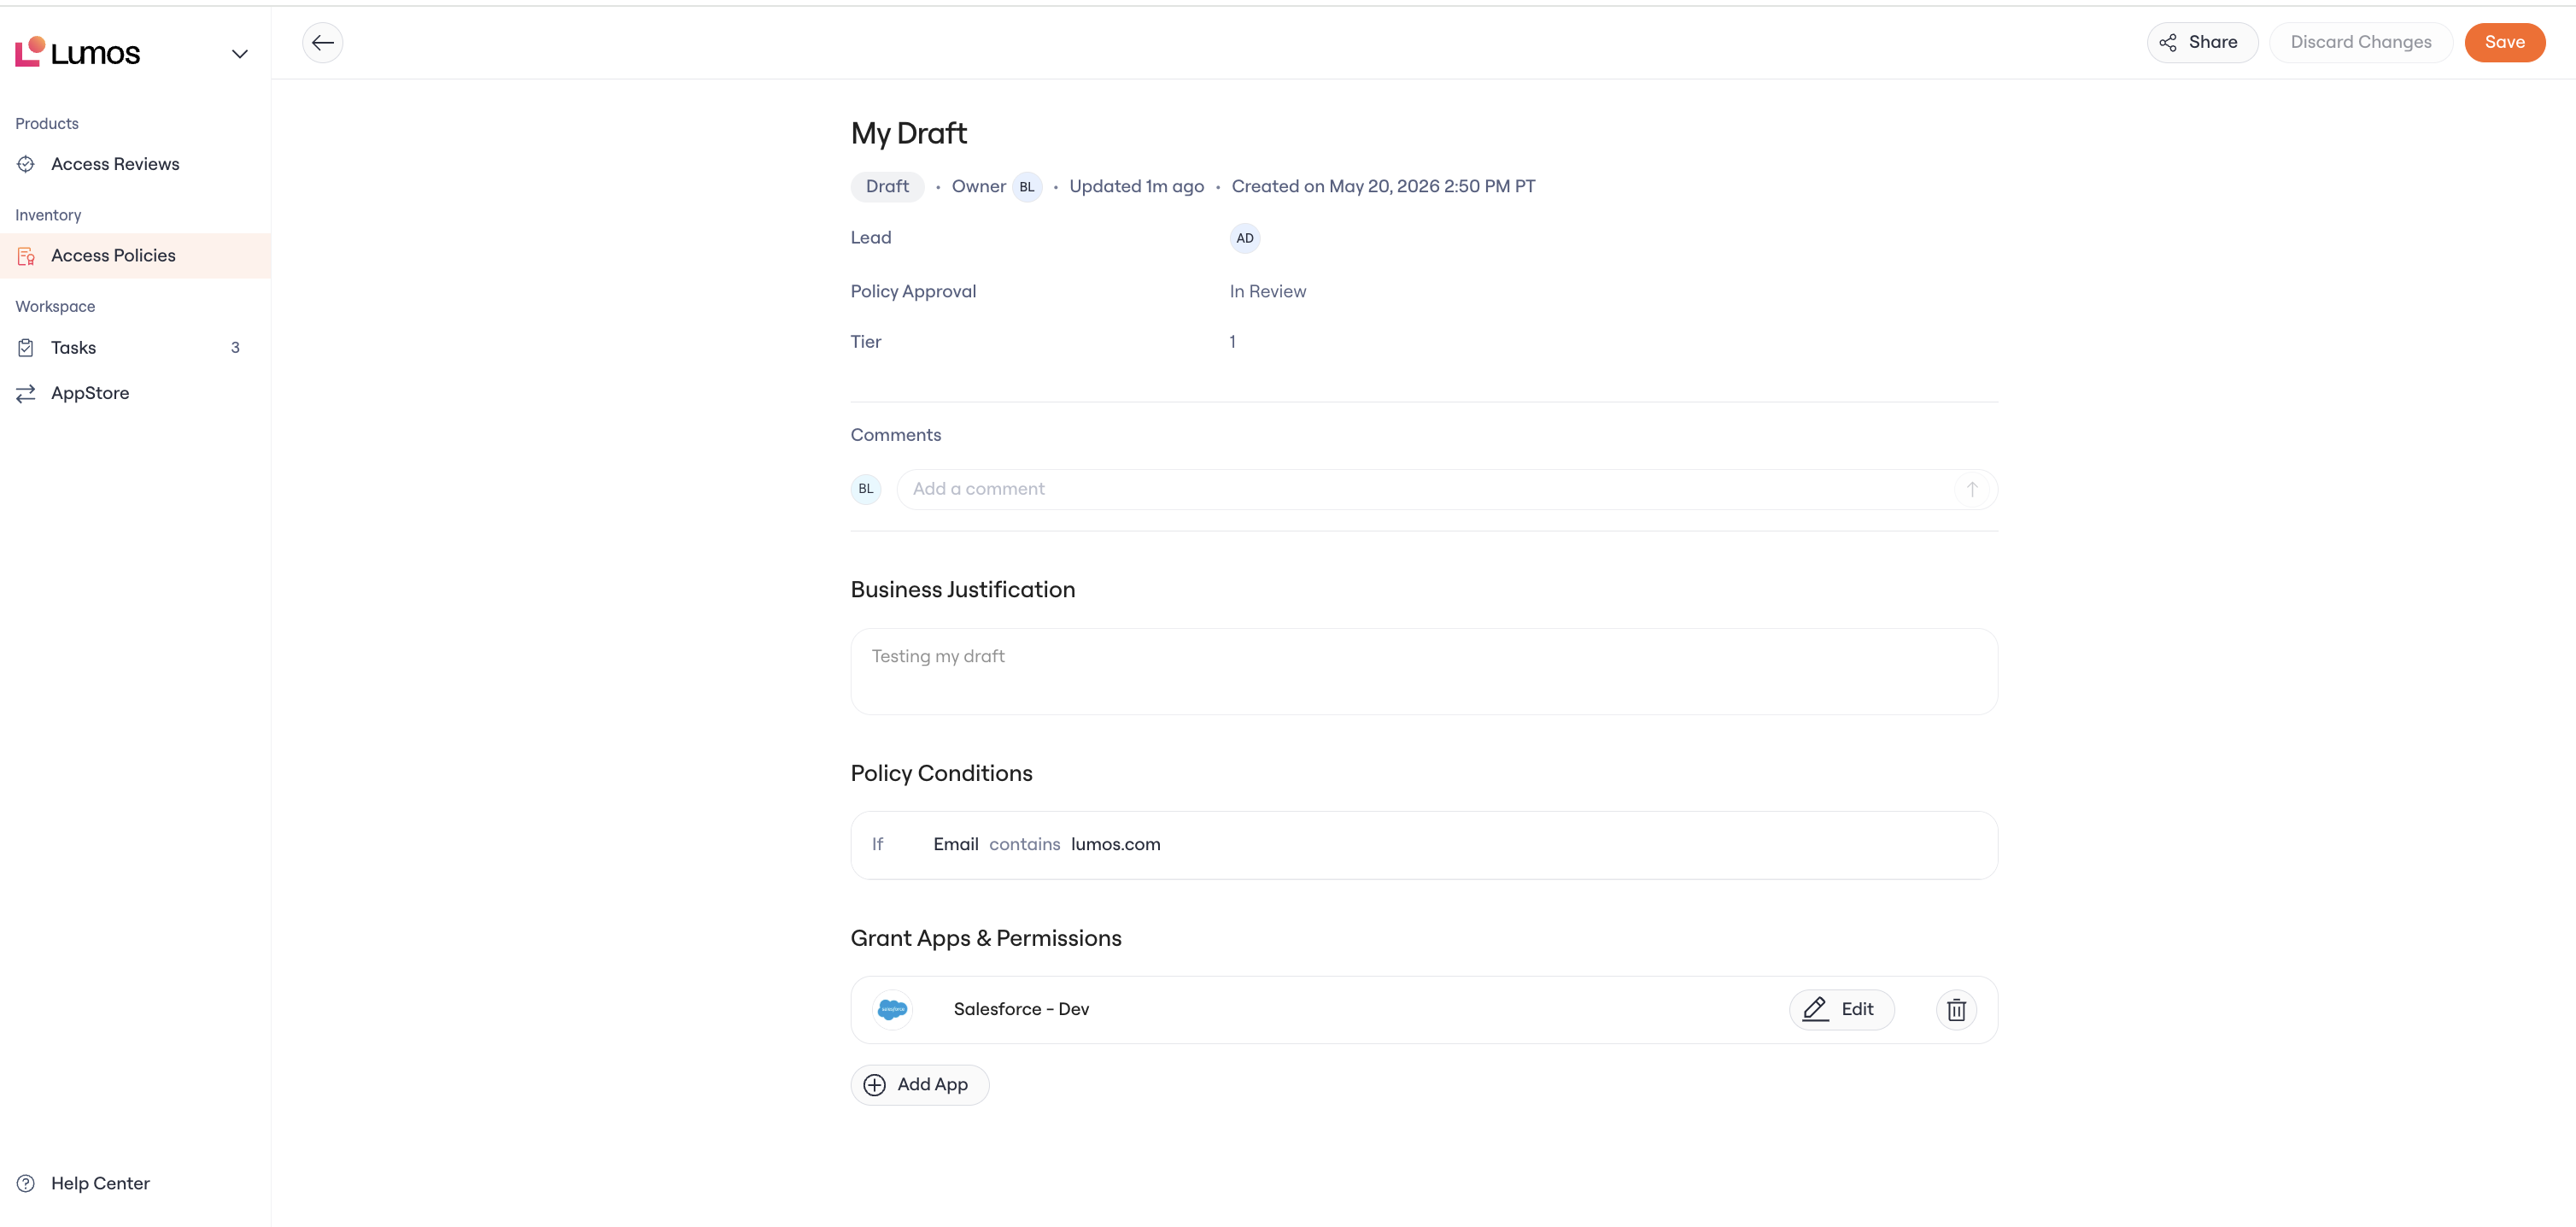
3. Answer one question for each grant
Should this policy be handing out the access you are responsible for? A few checks that make it quick:- Does everyone the policy covers really need this app or permission?
- Is the permission level right, or is it more than the job requires?
- Is there anything that should be requested case by case instead of granted automatically?
4. Leave your verdict as a comment
Comments are how your review is recorded.- If something should change, say what and why. Your comment is what the admin team acts on.
- If the policy is right as it stands, say that too. A silent review looks like an unfinished one.